

Account ownership
Define account ownership across organisational and supplier boundaries.
Enterprise engineering
When access is inconsistent, over-permissioned or difficult to recover, Kritical improves identity across Active Directory, Microsoft Entra ID and connected applications, so people and services get the access they need and nothing more than that.
On this page
Jump to the part that matches the problem or decision in front of you.
Microsoft positions Entra as a family of identity and network access products: Entra ID for authentication and provisioning, Conditional Access for adaptive policy enforcement, Permissions Management for least-privilege controls, and Verified ID for digital credentials. You don't have to guess which of those pieces you need turned on for your environment; we work that out against your real authentication paths, not the vendor's full feature list.
Start with the users, administrators, service accounts and application identities in scope. We identify where accounts originate, how access is granted and which authentication paths are in use. This baseline distinguishes a sign-in problem from a provisioning, policy or application dependency issue and provides the basis for a controlled change, including emergency access arrangements and a process for reviewing changes afterwards.
A project can address multi-factor authentication, Conditional Access, privileged access, federation or certificate-related dependencies. Controls need an operating process for enrolment, exceptions, recovery and departure. We test the impact on administrators, remote workers and service accounts rather than assuming a policy suitable for one group can be applied everywhere.
Identity changes often cross organisational and supplier boundaries. We define account ownership, synchronisation, application changes and the conditions for switching authentication paths.
Define account ownership across organisational and supplier boundaries.
Plan synchronisation and coexistence before changing authentication paths.
Identify the application changes needed to preserve access continuity.
Test recovery arrangements to the extent agreed in scope.
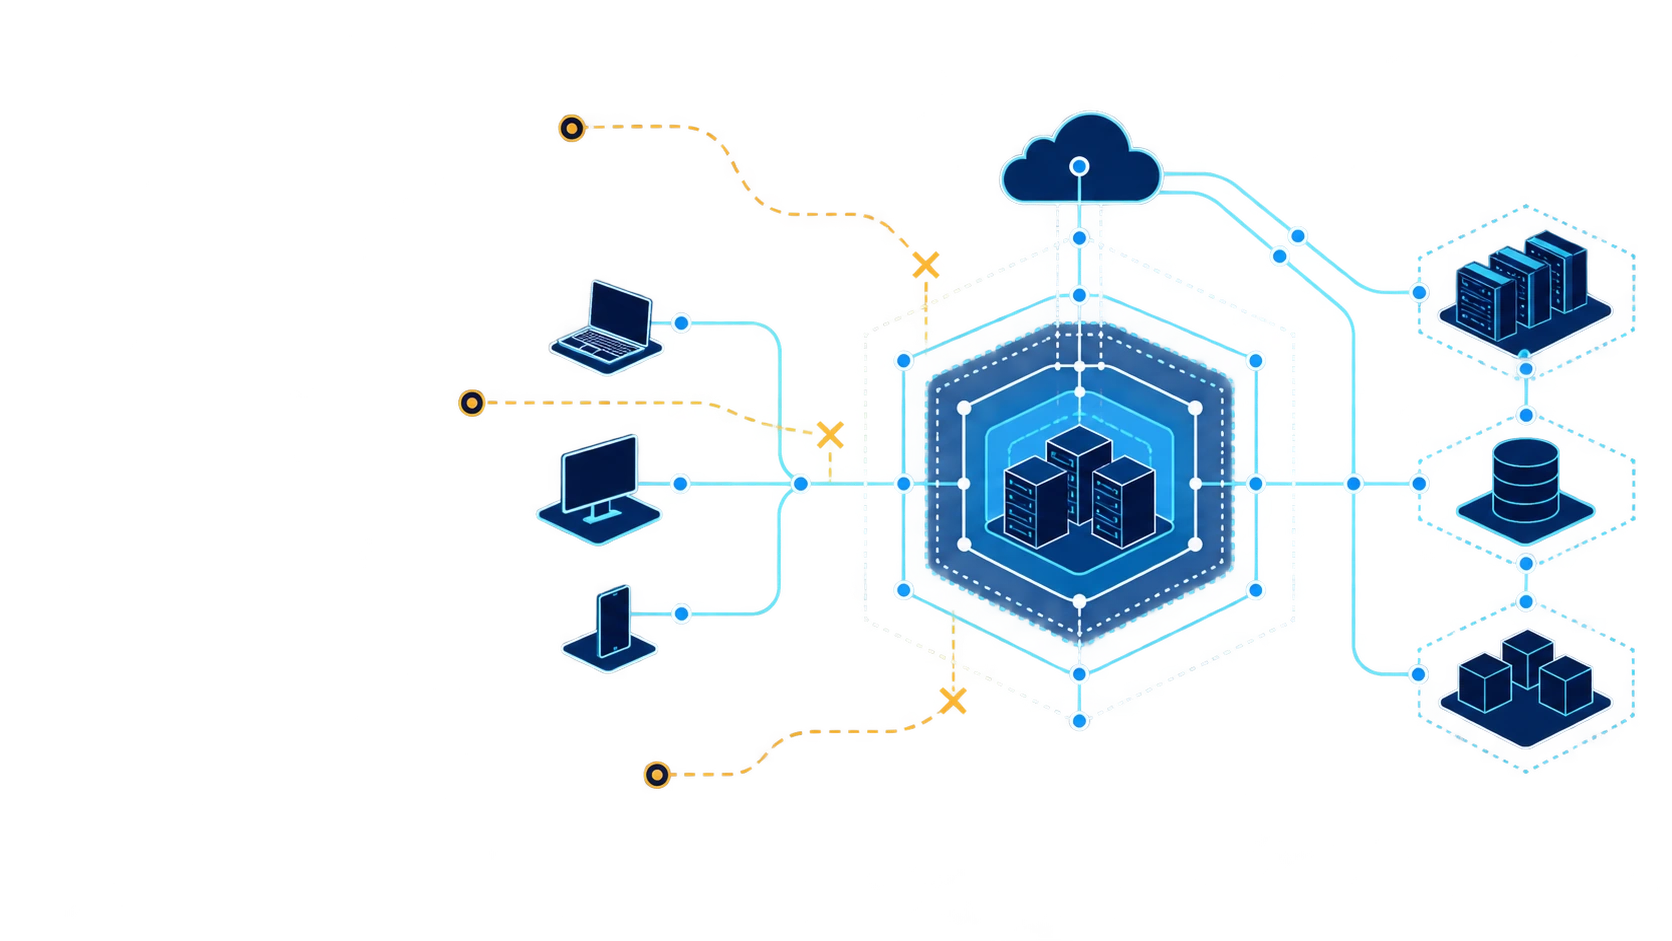
Active Directory, DNS, certificate authority services and Entra ID depend on each other. We design and repair them together instead of treating each as a separate ticket.
Resilient name resolution, including silent multimaster DNS and separate advertiser and resolver NLB clusters where the environment calls for them.
PKI that issues, renews and revokes certificates, with expiry tracked.
A scoped assessment or change is quoted in writing before work starts. Acceptance shows that intended users can complete required work and that restricted actions are controlled. Handover can include configuration records, test results, exception handling and access recovery procedures. Policy decisions and risk acceptance remain with your organisation; the engineering engagement records what was implemented and what still requires action.
Identity controls and application behaviour meet at the user journey. Make the responsibility boundary clear, then choose the evidence path that explains whether the problem is security, performance or both.
Use these guides to see which technologies can help with the job in front of you.
Workplace, identity, cloud and business applications, connected to a clear implementation or support requirement.
Device selection, deployment and lifecycle planning for Apple in the workplace.
Password management for shared logins, with fast removal of access when someone leaves.
Yes. Assessment and change work can include their hybrid relationship and the applications that depend on it.
A rollout needs impact assessment, testing, recovery arrangements and staged deployment where appropriate. The design addresses lockout risk before enforcement.
Include the certificate services, applications and renewal or trust issue in your enquiry. The scope depends on the platforms and responsibilities involved.
It comes down to which Conditional Access, identity protection and governance features you need. We check your current subscriptions before recommending a change.
Yes. The assessment starts by mapping current privileged accounts and their actual use before proposing any change to how they're controlled.
Kritical works on Windows infrastructure and the services business applications depend on, including Active Directory, hybrid identity and platform migration.
Kritical assesses and engineers Azure environments alongside the systems they connect to.
Kritical assesses configuration, prioritises remediation and implements agreed security improvements across identity, endpoints, networks and infrastructure.
Tell us what you want to achieve, what you have today and when it matters.